We are getting close to releasing BugBountyHunter v2 which will introduce a brand new website, including member platforms, new features, challenges, guides, videos, and the long awaited zseano methodology v2. Right now, all of the content on this website is considered out-dated, however our members section continues to operate for members.
Stay tuned for updates coming soon!
FirstBlood-#142 — IDOR on newly registered doctor
This issue was discovered on FirstBlood v1
On 2021-05-10, codersanjay Level 3 reported:
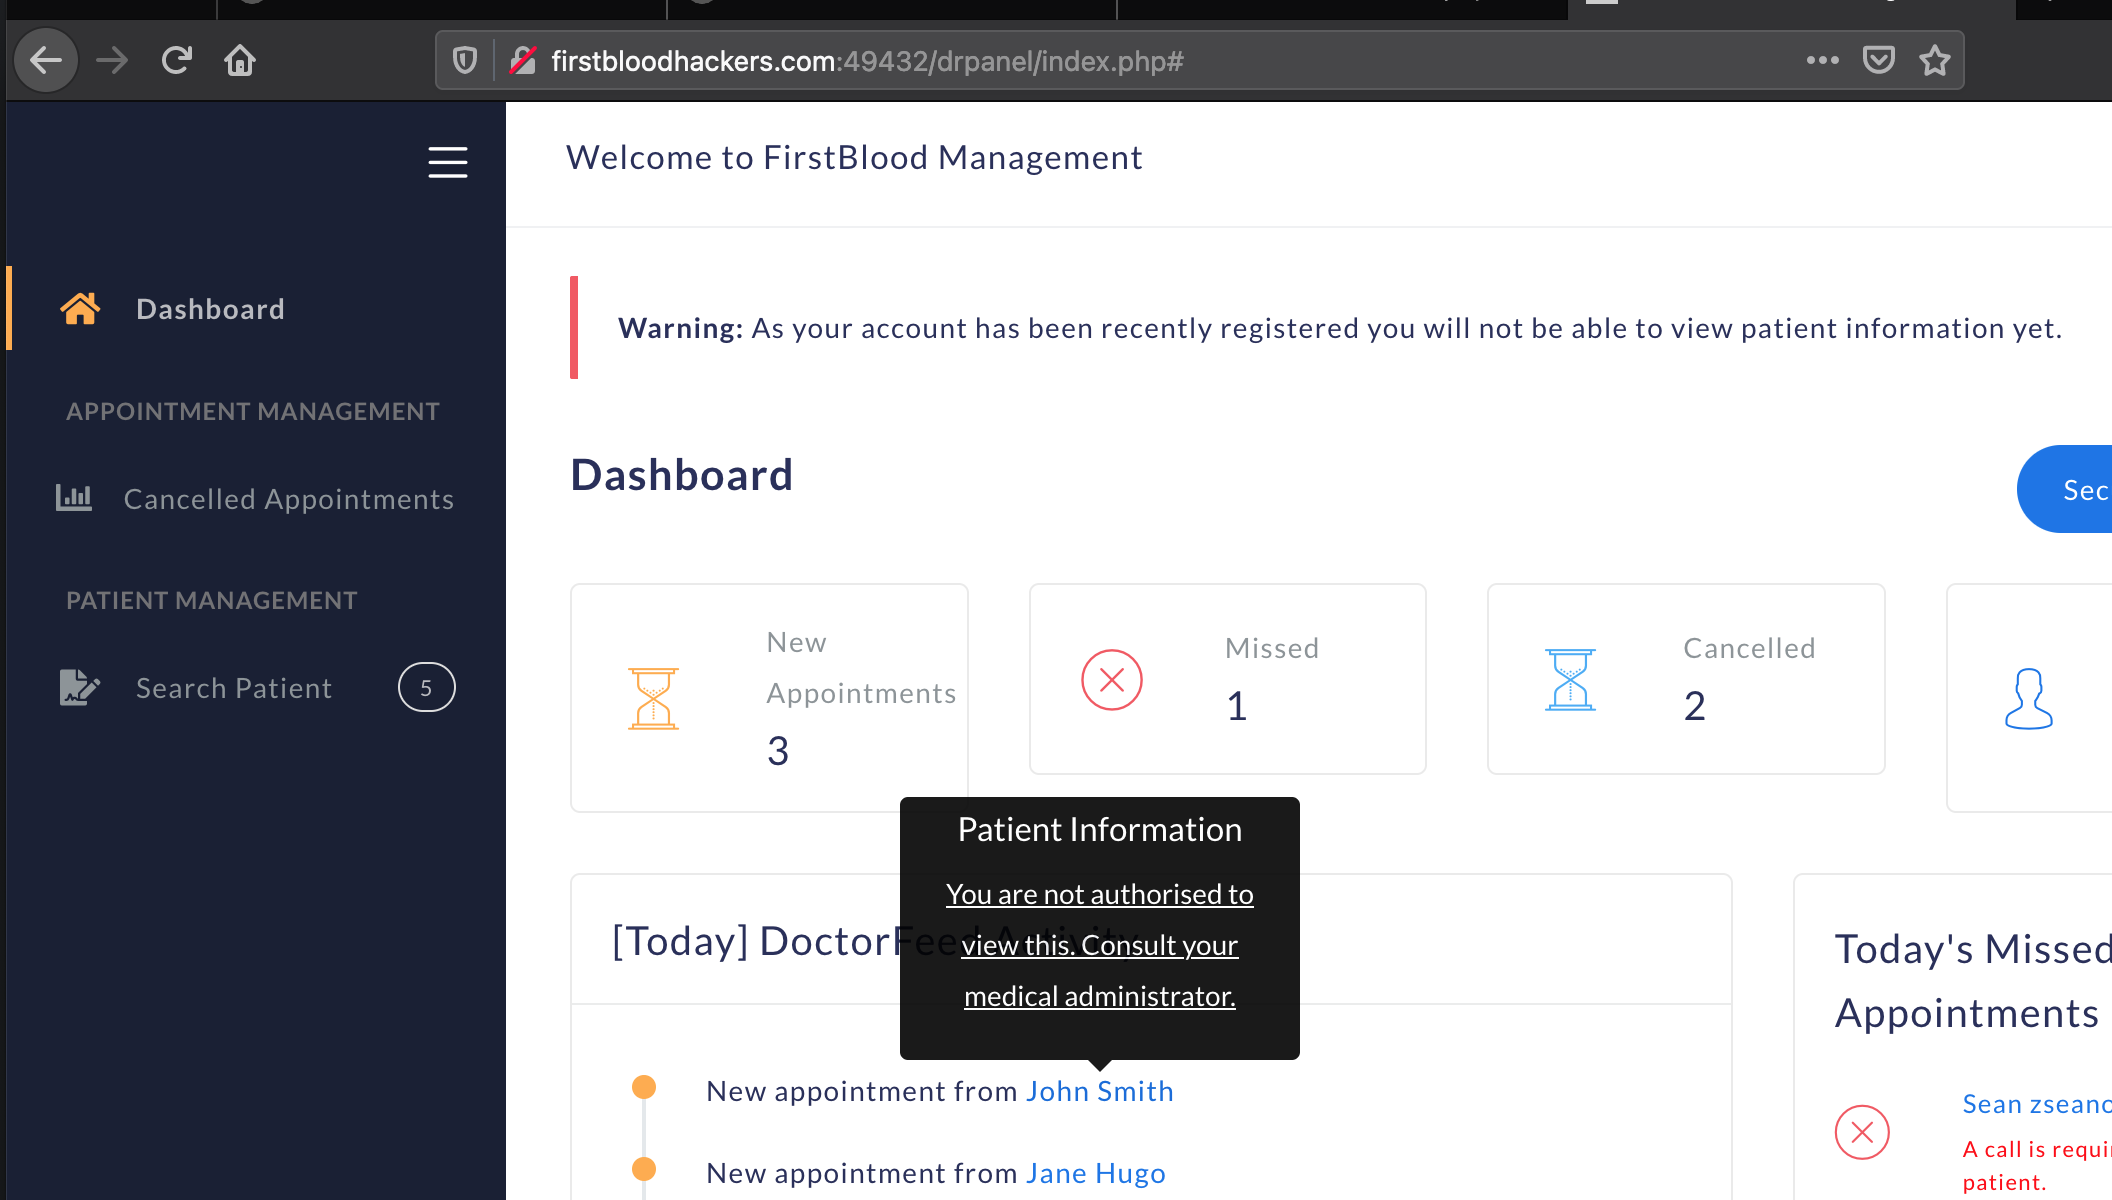
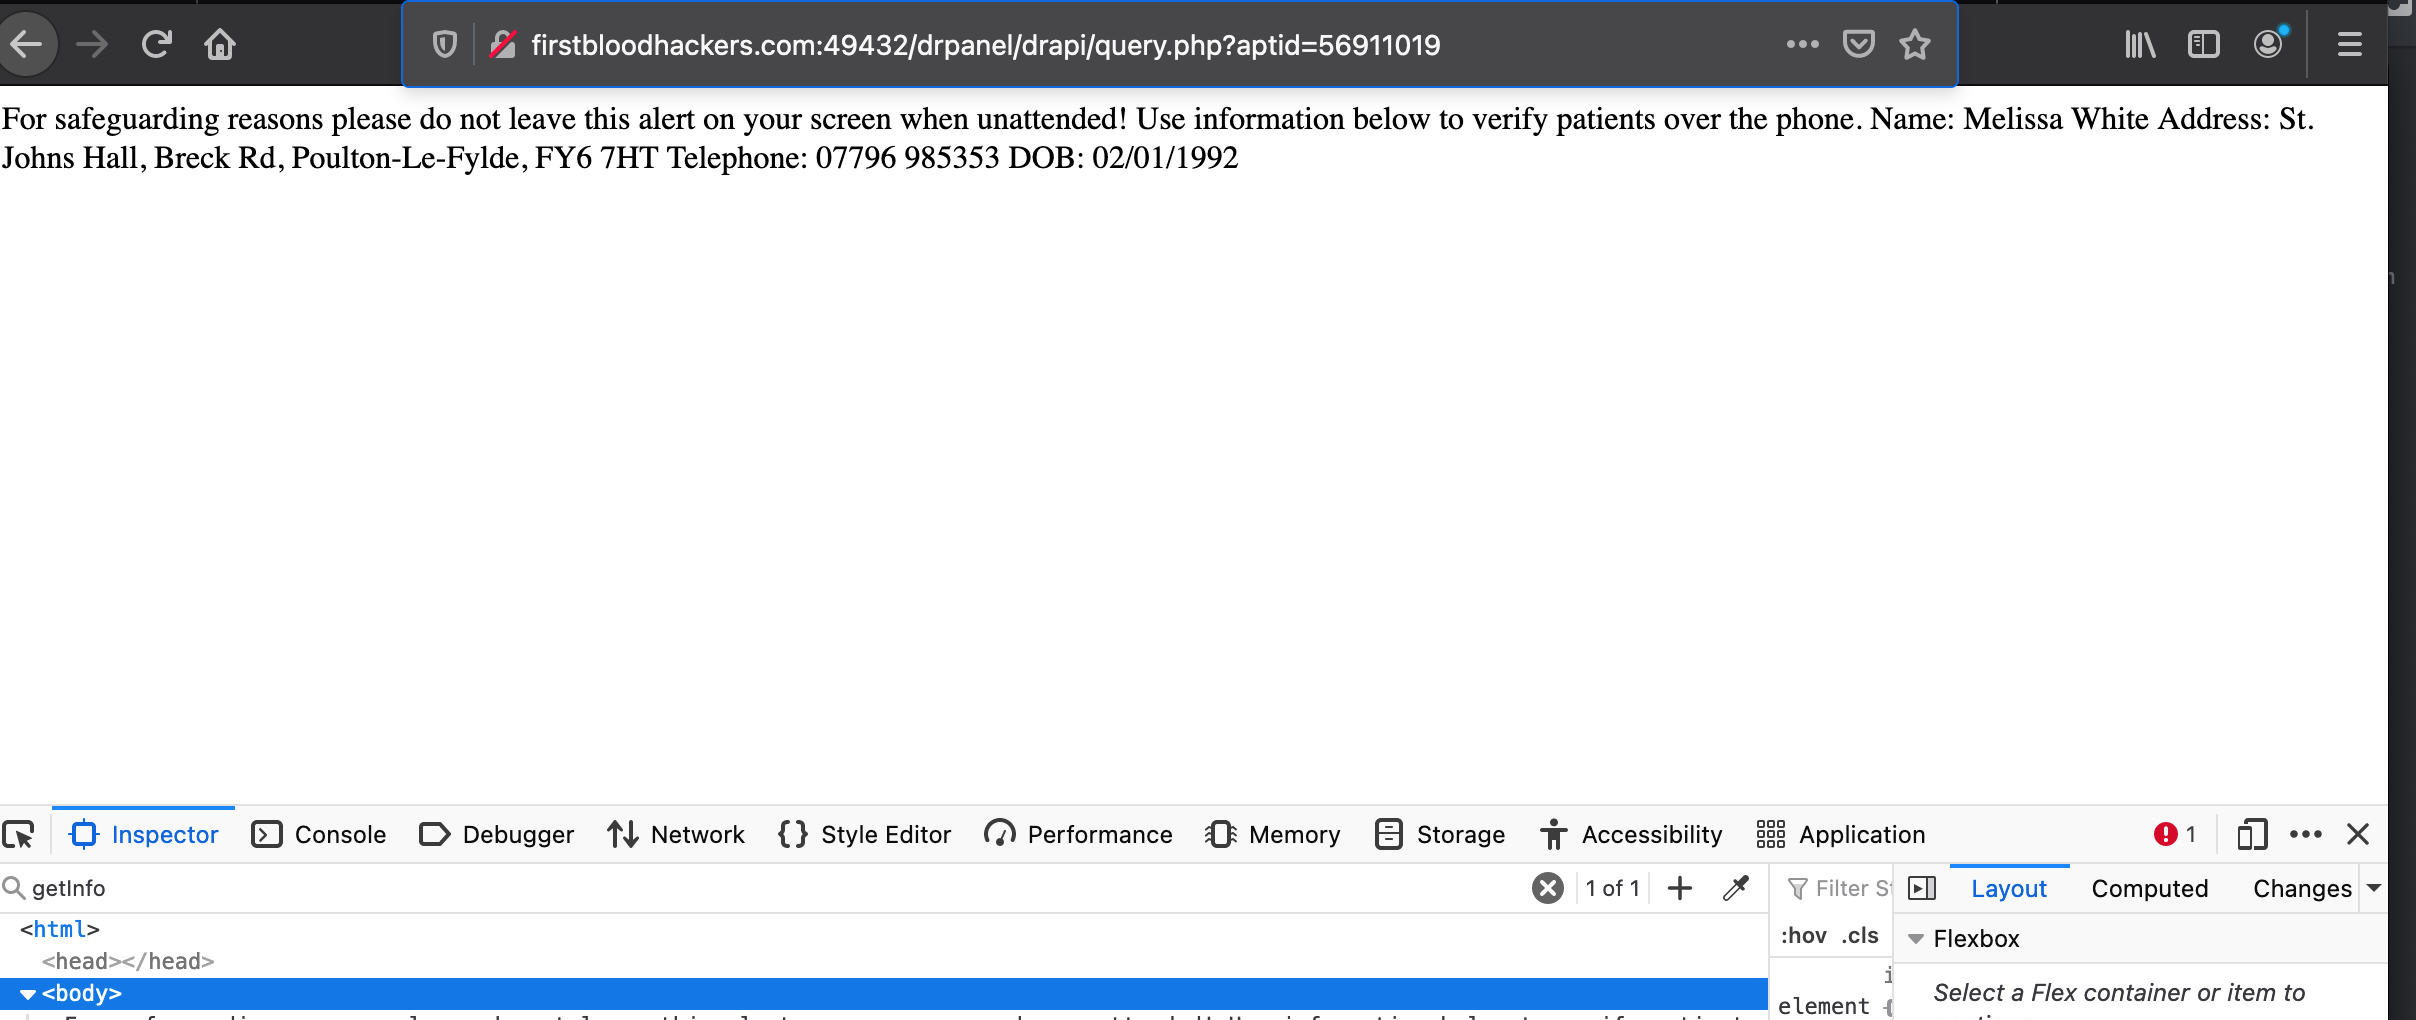
A newly registered doctor cannot see the patients info in general,
but with aptid known or randomly guessing, he can still get the patients info by just sending a GET request to
http://firstbloodhackers.com:49432/drpanel/drapi/query.php?aptid=56911019
Impact
PII leak
P1 CRITICAL
Endpoint: /drpanel/drapi/query.php
Parameter: aptid=56911019
Payload: aptid=56911019
FirstBlood ID: 11
Vulnerability Type: Application/Business Logic
Administrator endpoints can be accessed by non privileged doctor accounts which reveals sensitive patient information.
 Getting started
 Learn about vulnerability types
 Getting started in bug bounties
 Test your knowledge
 Free Web Application Challenges
 Guides for your hunts
 ZSeano's Methodology
 Effective Note Taking for bug bounties
 Useful Resources
 Disclosed HackerOne Reports
 Our community
 Endorsed Members
 Hackevents
 Member Articles